
From the artifact itself
Surveyor reads the built software, so it finds PHP in vendor images and backups as well as on your own servers. It needs no source code and no agent on the server.
PHP2Shell is two critical flaws in PHP that let anyone run code on a web server without logging in, and attackers are already using them. Spice Labs Surveyor finds the vulnerable PHP binaries in the built software you run, with no source code needed.
PHP2Shell is two critical flaws in PHP, CVE-2026-109618 and CVE-2026-109619, each rated CVSS 9.2. Both allow unauthenticated remote code execution on any PHP that serves web requests: PHP-FPM, Apache mod_php, php-cgi, FrankenPHP and LiteSpeed. Exploitation began on October 17, 2026, before the flaws were disclosed, and it is now broad. The fixed releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team says only updating fully protects a server.
Linux distributions often patch PHP without changing its version number, so a version check can mislead. The exact binary on disk is the evidence that settles it.
In the video, Surveyor OT Pro sweeps three web server disk images and finds the vulnerable PHP binaries. It matches the php, php-cgi, php-fpm and libphp binaries by hash against a list of known vulnerable builds. It needs no source code and runs on a machine with no network.
How long did it take you to find every vulnerable copy of PHP?
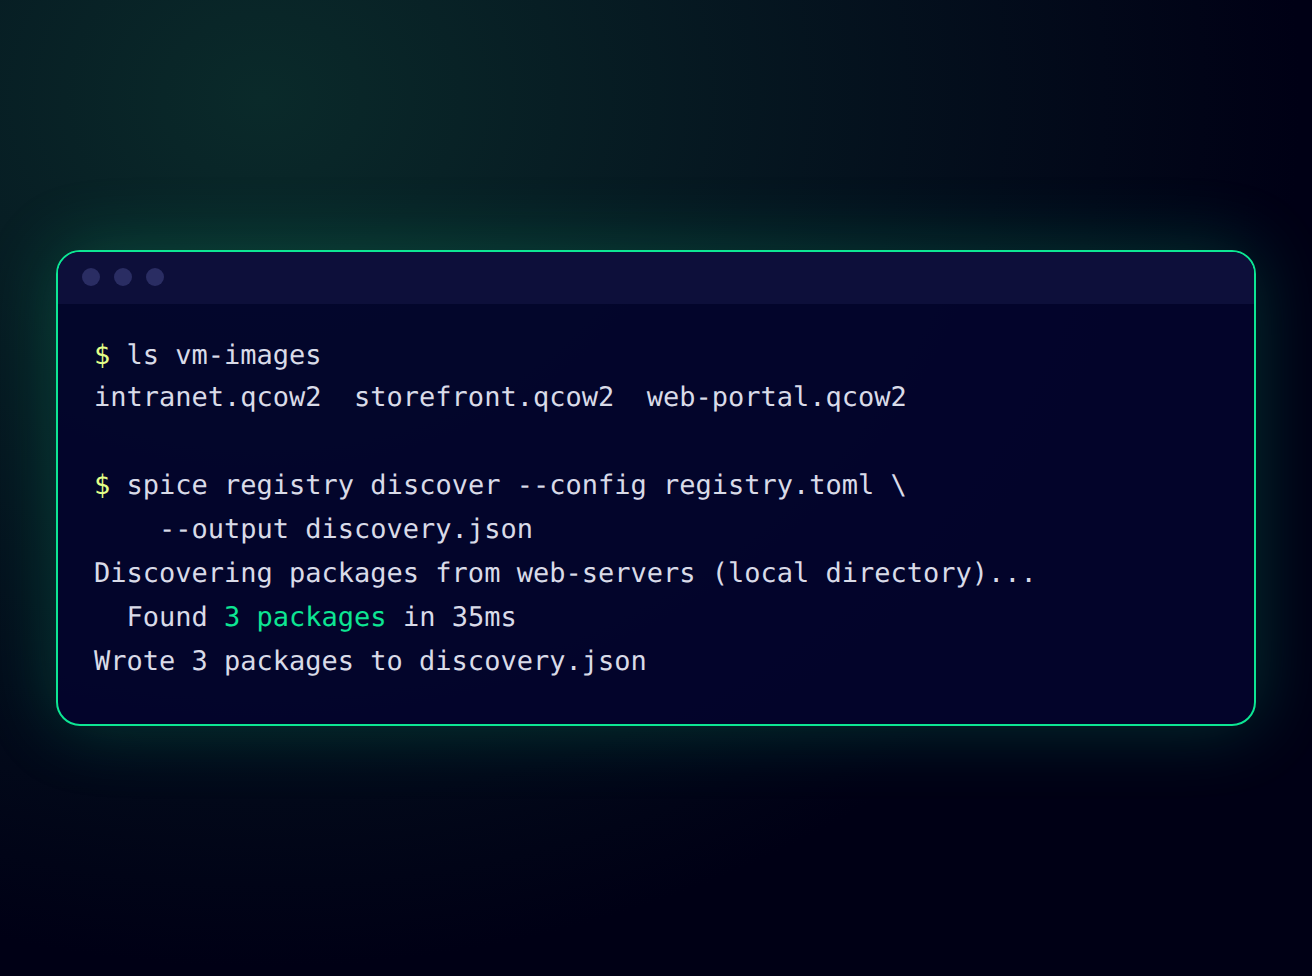
Give Surveyor the built software: VM disk images, backups, container images and firmware. It opens the file systems, archives and container images inside them.
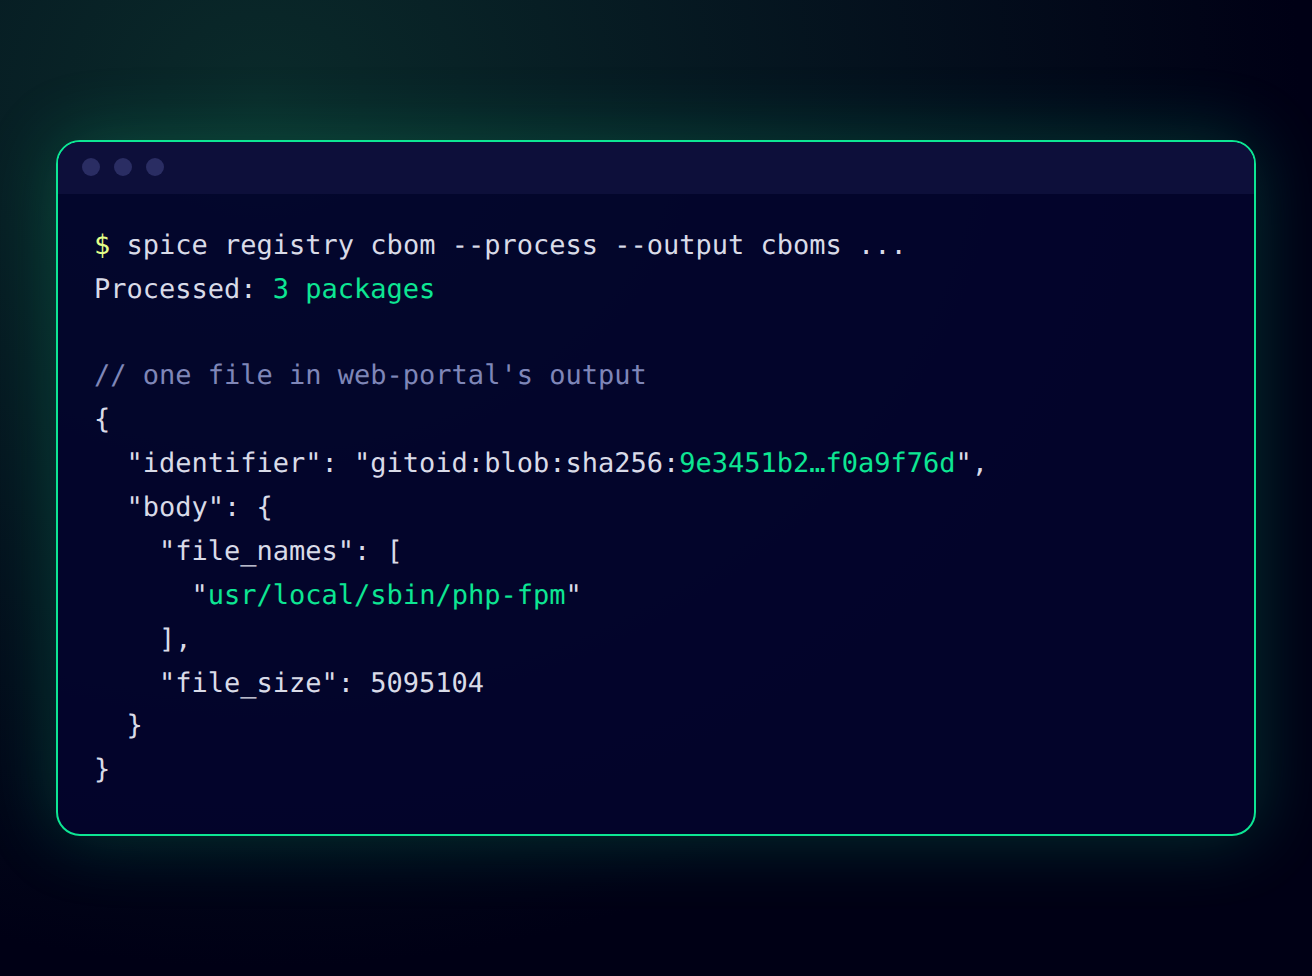
Surveyor maps each image down to its individual files. It records a hash for every file it finds, along with the path to that file inside the image.
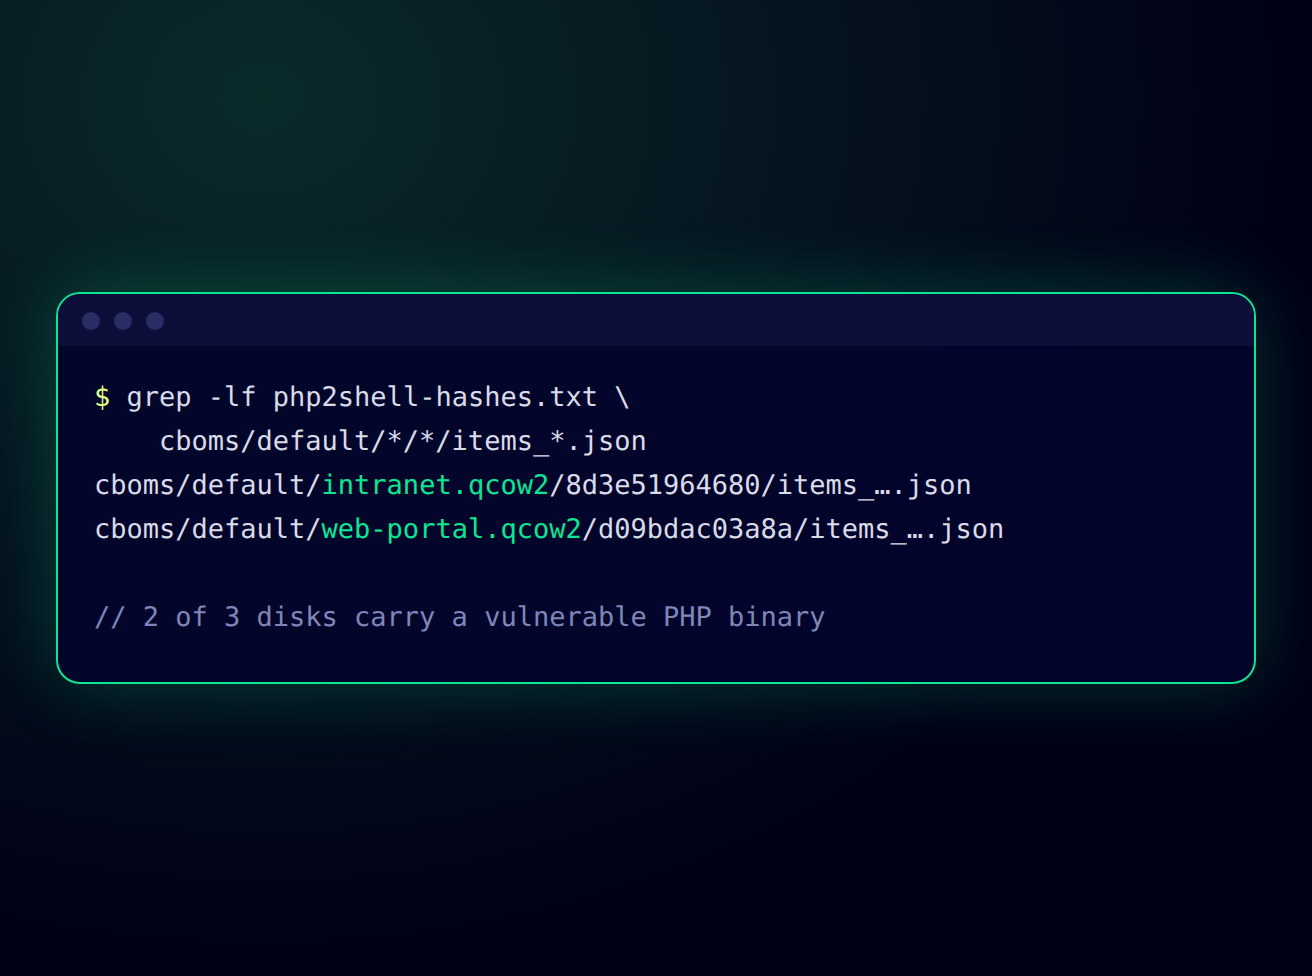
Search Surveyor’s output for the hashes of known vulnerable php, php-cgi, php-fpm and libphp builds from the Linux distributions and FreeBSD. Every match names the image that carries one and where inside that image it sits.
Distributions are still shipping their fixed PHP builds, and the list of known vulnerable builds grows as more are checked. Surveyor’s record of every file stays on your machine, so checking again after each update is a quick search of the record you already have.
Every unpatched PHP that serves web requests is exposed, whether it runs under PHP-FPM, Apache mod_php, php-cgi, FrankenPHP or LiteSpeed. Surveyor finds the vulnerable builds in your VM disk images, backups and container images.
Network appliances, storage systems and industrial consoles often serve their web admin pages with PHP. Surveyor OT Pro reads their disk images and firmware on a machine with no network, and nothing leaves that machine.
When a flaw is exploited before it is disclosed, the first question is which of your servers are affected. A search of Surveyor’s output answers it with a list you can act on.
Surveyor reads the built software, so it finds PHP in vendor images and backups as well as on your own servers. It needs no source code and no agent on the server.
A version number can hide a distribution’s patch. Surveyor matches the php, php-cgi, php-fpm and libphp binaries by hash, across distributions and chip types.
Surveyor OT Pro runs on a machine with no network. Your images and results stay on the machine you run it on.
Tell us what you run, and we’ll help you find the vulnerable PHP in it. Reporters covering PHP2Shell can reach us the same way.
Surveyor OT Pro finds the PHP2Shell vulnerable PHP
PHP patches the PHP2Shell vulnerabilities, CVE-2026-109618 and CVE-2026-109619
Amazon threat intelligence saw PHP2Shell exploited before public disclosure
PHP issues emergency patches for two critical flaws
PHP announces a critical security release for two vulnerabilities
Disk images, containers and the other file types Surveyor reads
Your first offline survey with Surveyor OT Pro or Surveyor IT Pro